#malware

WhatsApp phishing campaign exploits trusted contacts to install rogue RMM agents
A global malware campaign is leveraging compromised WhatsApp accounts to distribute malicious VBScript files disguised as financial documents. Attackers target users of WhatsApp Desktop and WhatsApp Web, sending attachments like "Financial Reports.vbs" to the…

WhatsApp VBScript Campaign Uses Fake Documents to Install ManageEngine RMM Tool
Direct messages sent via WhatsApp are being used to distribute malicious Visual Basic Script (VBScript) files that lead to the installation of legitimate Remote Monitoring and Management (RMM) software. Per findings from Kaspersky, the active campaign is tar…

As the World Cup Begins, the Internet Enters Its Own High-Stakes Tournament of Scams
This week in cybersecurity saw a surge of World Cup-related scams, malware hidden in gaming tools, a fake breach-reporting incident that briefly disrupted a state portal, and more. The World Cup is here, which is great news for fans (and my social media feeds…

Operation Endgame Disrupts SocGholish Servers, Cleans 14,971 WordPress Sites
Dutch law enforcement authorities, along with counterparts from Canada , Germany, and the U.S., have disrupted malicious infrastructure associated with SocGholish and cleaned up nearly 15,000 infected WordPress websites. "With these actions we deprive cyberc…

Anime Girls Could Steal Your Crypto as Wallpaper Malware Targets Steam Gamers
Researchers found malicious Wallpaper Engine downloads on Steam Workshop distributing infostealers, backdoors, and account-hijacking malware.

As the World Cup Begins, the Internet Enters Its Own High-Stakes Tournament of Scams
This week in cybersecurity saw a surge of World Cup-related scams, malware hidden in gaming tools, a fake breach-reporting incident that briefly disrupted a state portal, and more. The World Cup is here, which is great news for fans (and my social media feeds…
Kaspersky finds malware hidden in Steam Wallpaper Engine that hijacks accounts to spread itself — dozens of malicious packages downloaded tens of thousands of times
Attackers have spent the past several months smuggling malware into Steam through animated desktop wallpapers.
Microsoft's GitHub confirms cyberattack involving unauthorised access of nearly 3,800 repositories
GitHub has confirmed a cyberattack after a threat actor claimed to have stolen and listed company data for sale. The breach involved unauthorised access to internal repositories via a "poisoned" VS Code extension, with the attacker's claims of accessing nearl…

Microsoft Takes Down Malware-Signing Service Behind Ransomware Attacks
Microsoft on Tuesday said it disrupted a malware-signing-as-a-service (MSaaS) operation that weaponized the company's Artifact Signing system to deliver malicious code and conduct ransomware and other attacks, compromising thousands of machines and networks a…
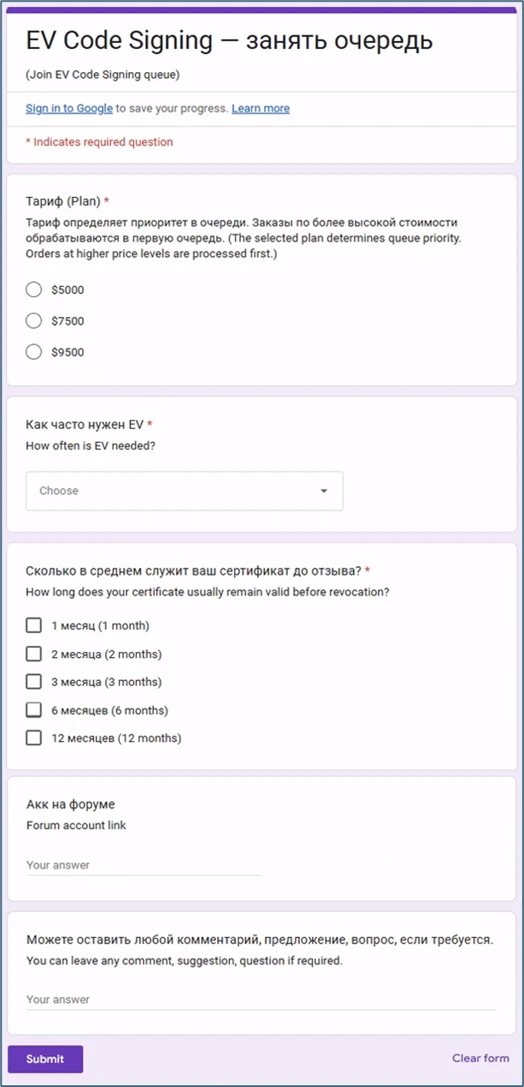
Microsoft dismantled malware-signing network Fox Tempest
Microsoft disrupted Fox Tempest, a malware-signing-as-a-service (MSaaS) that allowed attackers to sign malware with fake trusted certificates. Microsoft said it disrupted a cybercrime operation run by a threat actor named Fox Tempest, which helped threat acto…

Exposing Fox Tempest: A malware-signing service operation
Fox Tempest is a financially motivated threat actor operating a malware‑signing‑as‑a‑service (MSaaS) used by other cybercriminals, including Vanilla Tempest and Storm groups, to more effectively distribute malicious code, including ransomware. The post Exposi…
Microsoft disrupts cybercrime service offering malware disguised as legitimate software
The downstream impact of that service’s operations “has resulted in attacks against a broad range of industry sectors” in the U.S. and other nations, the company said.

IT threat evolution in Q1 2026. Non-mobile statistics
The report presents key trends and statistics on malware that targeted personal computers running Windows and macOS, as well as Internet of Things (IoT) devices, during Q1 2026.

New Malware Builder Targets 700+ Banks Across the Globe, Allows Thieves To Steal Credentials and Take Over Accounts: Report
A new malware-as-a-service threat is targeting hundreds of banks around the world by giving cybercriminals tools to steal credentials and take over accounts. According to a new advisory from the cybersecurity firm iZOO Logic, the threat was identified as a Te…

Fake income tax emails target Indians: Kaspersky warns of ‘SilverFox’ hacker attack
Cybersecurity firm Kaspersky has warned Indian consumers about a sophisticated phishing campaign by the SilverFox hacker group. These malicious emails, disguised as official Income Tax Department notices, aim to trick users into downloading malware. The attac…